> For the complete documentation index, see [llms.txt](https://help.tellius.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://help.tellius.com/tellius-6.4/settings/users-and-access/users.md).
# Users
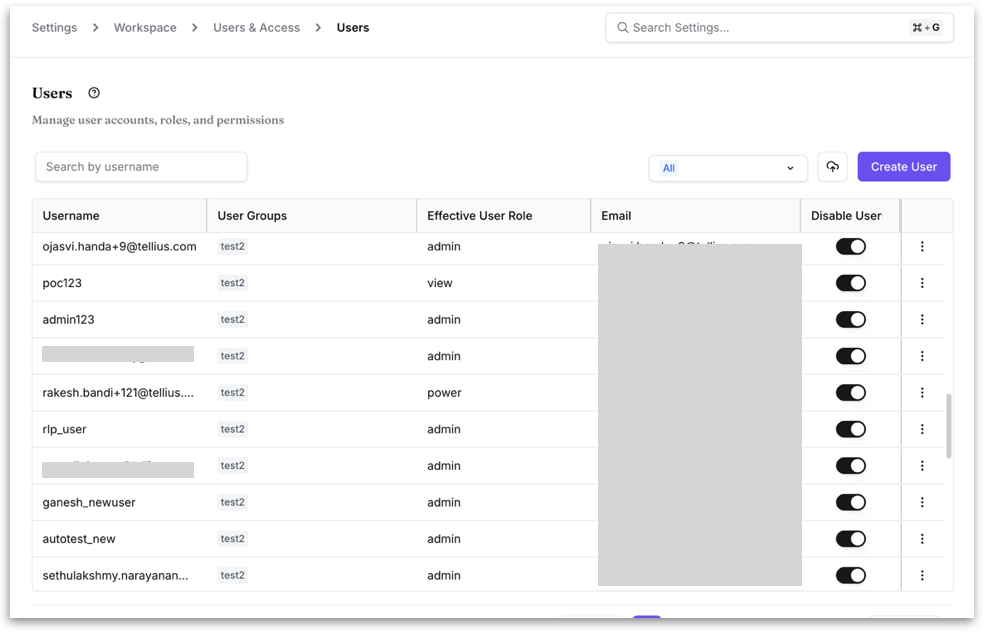
Under **Settings → Workspace → Users & Access → Users**, you manage everyone who can sign in to your workspace — creating accounts, setting roles, controlling group membership, and switching access on or off.
**Finding users:** Use *Search by username* to jump to a specific person. Two dropdowns narrow the list. The first filters by assigned role, and lists the built-in roles followed by any [custom roles](https://help.tellius.com/settings/users-and-access/custom-roles). The second filters by status: **All**, **Enabled** or **Disabled**.
The table shows each user's **Username**, their **User Groups**, their **Assigned Role**, their **Roles in Effect** and their **Email**. **Assigned Role** is the role set on the user. **Roles in Effect** lists every role that gives the user access: their own role, plus the role of each group they belong to. The **Status** toggle switches a person's access off without deleting their account, and back on whenever you need.
**Export:** the export icon beside the status filter downloads the users that match your current search and filters. If no filters are applied, every user is exported. If you have selected users, only the selected users are exported.
### Select several users
Tick the checkbox beside each user you want to work with, or tick the checkbox in the header to select everyone on the page. A bar above the table shows how many users are selected and offers these actions:
* **Select all … matching:** extend the selection to every user that matches your search and filters, on every page.
* **Enable:** turn the selected users on.
* **Assign Group:** add the selected users to a group.
* **Disable:** turn the selected users off, without deleting their accounts.
* **x:** clear the selection.
### Import config
**Import config** beside **Create User** updates many existing users at once from a single file, instead of one person at a time. It offers two imports:
* **Personalization:** set personalized filters for existing users.
* **Security Tags:** set security tag assignments for existing users. See [Security Tags](https://help.tellius.com/settings/users-and-access/security-tags).
Both run in three steps: **Upload File**, **Map Users** and **Map Columns**. The file can be .xlsx, .xls or .csv, one file at a time, up to 10 MB. For the personalized filter steps, see [Step 4](https://help.tellius.com/vizpads-explore/tag-based-personalized-filters#step-4-optional-bulk-upload-personalization-for-many-users) of Tag-based personalized filters.
### **How to create a new user**
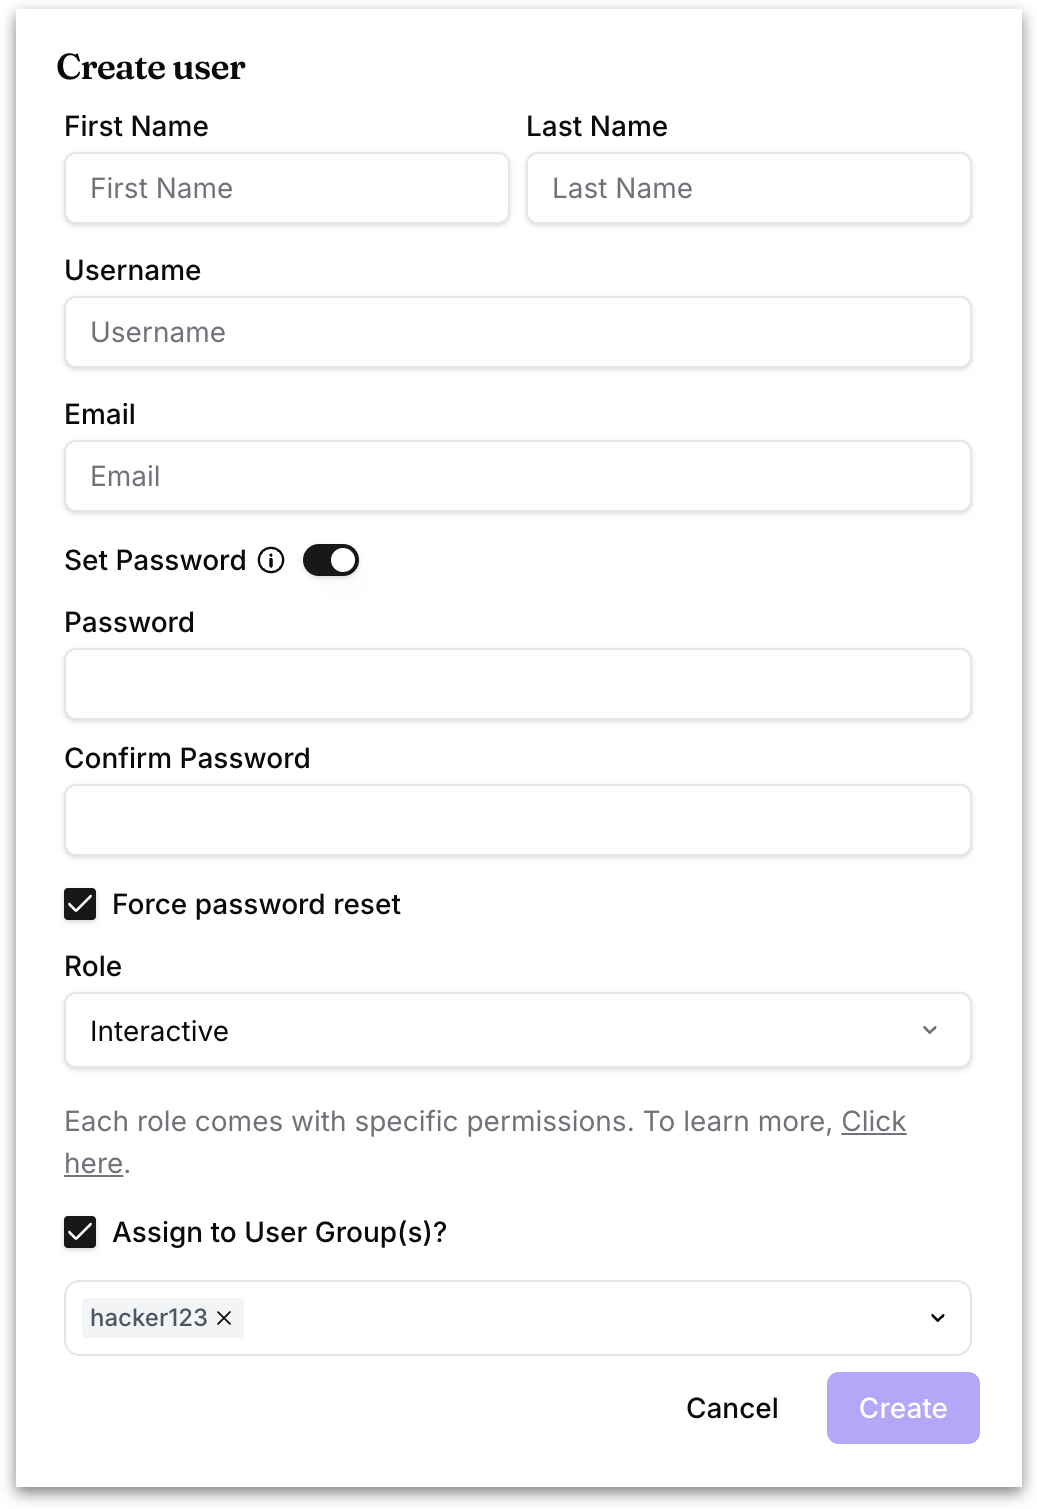
Click on **Create User** and the following window will be displayed.
* **First Name / Last Name:** Editable fields for the user’s display name.
* **Username:** A unique identifier for the user’s login and internal reference.
* **Email:** Used for login, notifications, password recovery, and system alerts.
* **Set Password:** Turn this on to give the user a password, then enter it in **Password** and **Confirm Password**. A password needs at least 8 characters, with at least one uppercase letter and one special character, mixing letters and numbers. Leave **Set Password** off for a user who signs in only through single sign-on.
* **Effective User Role:** Shown when you edit a user. A read-only field with the highest role the user receives from their own role and the roles of the groups they belong to. Tellius uses it to decide what content the user can reach.
* **Change Password:** Shown when you edit a user. Opens a dialog to set or reset the user's password.
* **Force password reset (checkbox):** If checked, the user will be required to change their password the next time they log in.
* **Role:** A dropdown that assigns a role to the user. It lists the built-in roles and any custom roles. A user holds one assigned role at a time, so choosing a new role replaces the one they had.
{% hint style="warning" %}
To know more about roles and their permissions, check out [User roles and permissions](https://help.tellius.com/settings/users-and-access/user-roles-and-permissions). To build your own roles, see [Custom roles](https://help.tellius.com/settings/users-and-access/custom-roles).
{% endhint %}
* **Assign to user group(s):** When checked, enables group assignment for the user. The group selector is a searchable dropdown for assigning one or more groups to the user.
{% hint style="info" %}
Assign users to at least one group for proper access control.
{% endhint %}
* **Create:** creates the user. When you edit a user, this button is **Save** and saves your changes to the user's profile. **Cancel** closes the dialog without saving.
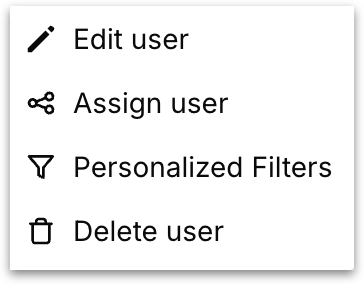
**Managing a user:** Each row's three-dot menu offers:
* **Edit user:** update the user's details or role.
* **Assign user:** transfer the user's content to another user. See [How to assign content of one user to another](#how-to-assign-content-of-one-user-to-another).
* **Personalized Filters:** set the row-level filters that decide which data the person sees by default.
* **Security Tags:** set the security tag values for the user. Select **Add Filter**, choose a **Security Tag** and an **Operator** (**In**, **Contains**, **Not in** or **Equals**), enter one or more **Values**, and select **ADD**.
* **View effective access:** see what the user can reach in each module, and which role gives it. See [View a user's effective access](#view-a-users-effective-access).
* **Delete user:** permanently remove the account.
### View a user's effective access
A user can receive access from their own role and from the role of each group they belong to. For each module, the highest level applies. **View effective access** shows the result: each module's level for the user, grouped by module heading, with a count of the modules at each level. Point to a module to see which roles and groups grant it, and which one sets the level. Use it to check what someone can do before you change a role or a group.
Users can also open the same view for themselves from [My Profile](https://help.tellius.com/settings/my-profile-1). For every part of the dialog, see [Check what a user can do](https://help.tellius.com/settings/users-and-access/custom-roles#check-what-a-user-can-do).
### How to assign content of one user to another
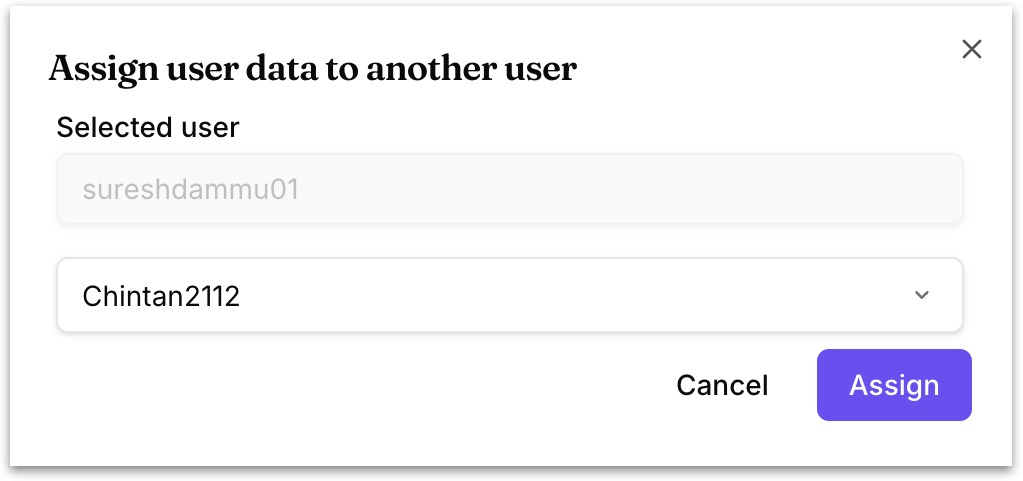
The following **Assign user** window allows admins to transfer all owned content and data assets from one user to another. It's commonly used when deactivating a user or reassigning responsibilities.
**Selected User:** A read-only field that displays the username of the person whose data is being reassigned.
**Target User:** Enter the username of the person who should receive the data.
Click on **Assign** to transfer the ownership from the selected user to the target user. Click on **Cancel** to close the dialog without making any changes.
{% hint style="warning" %}
This operation does not delete the selected user; it only transfers asset ownership. Once data is reassigned, it may no longer be visible or accessible from the original owner’s profile.
{% endhint %}
### How to delete a user
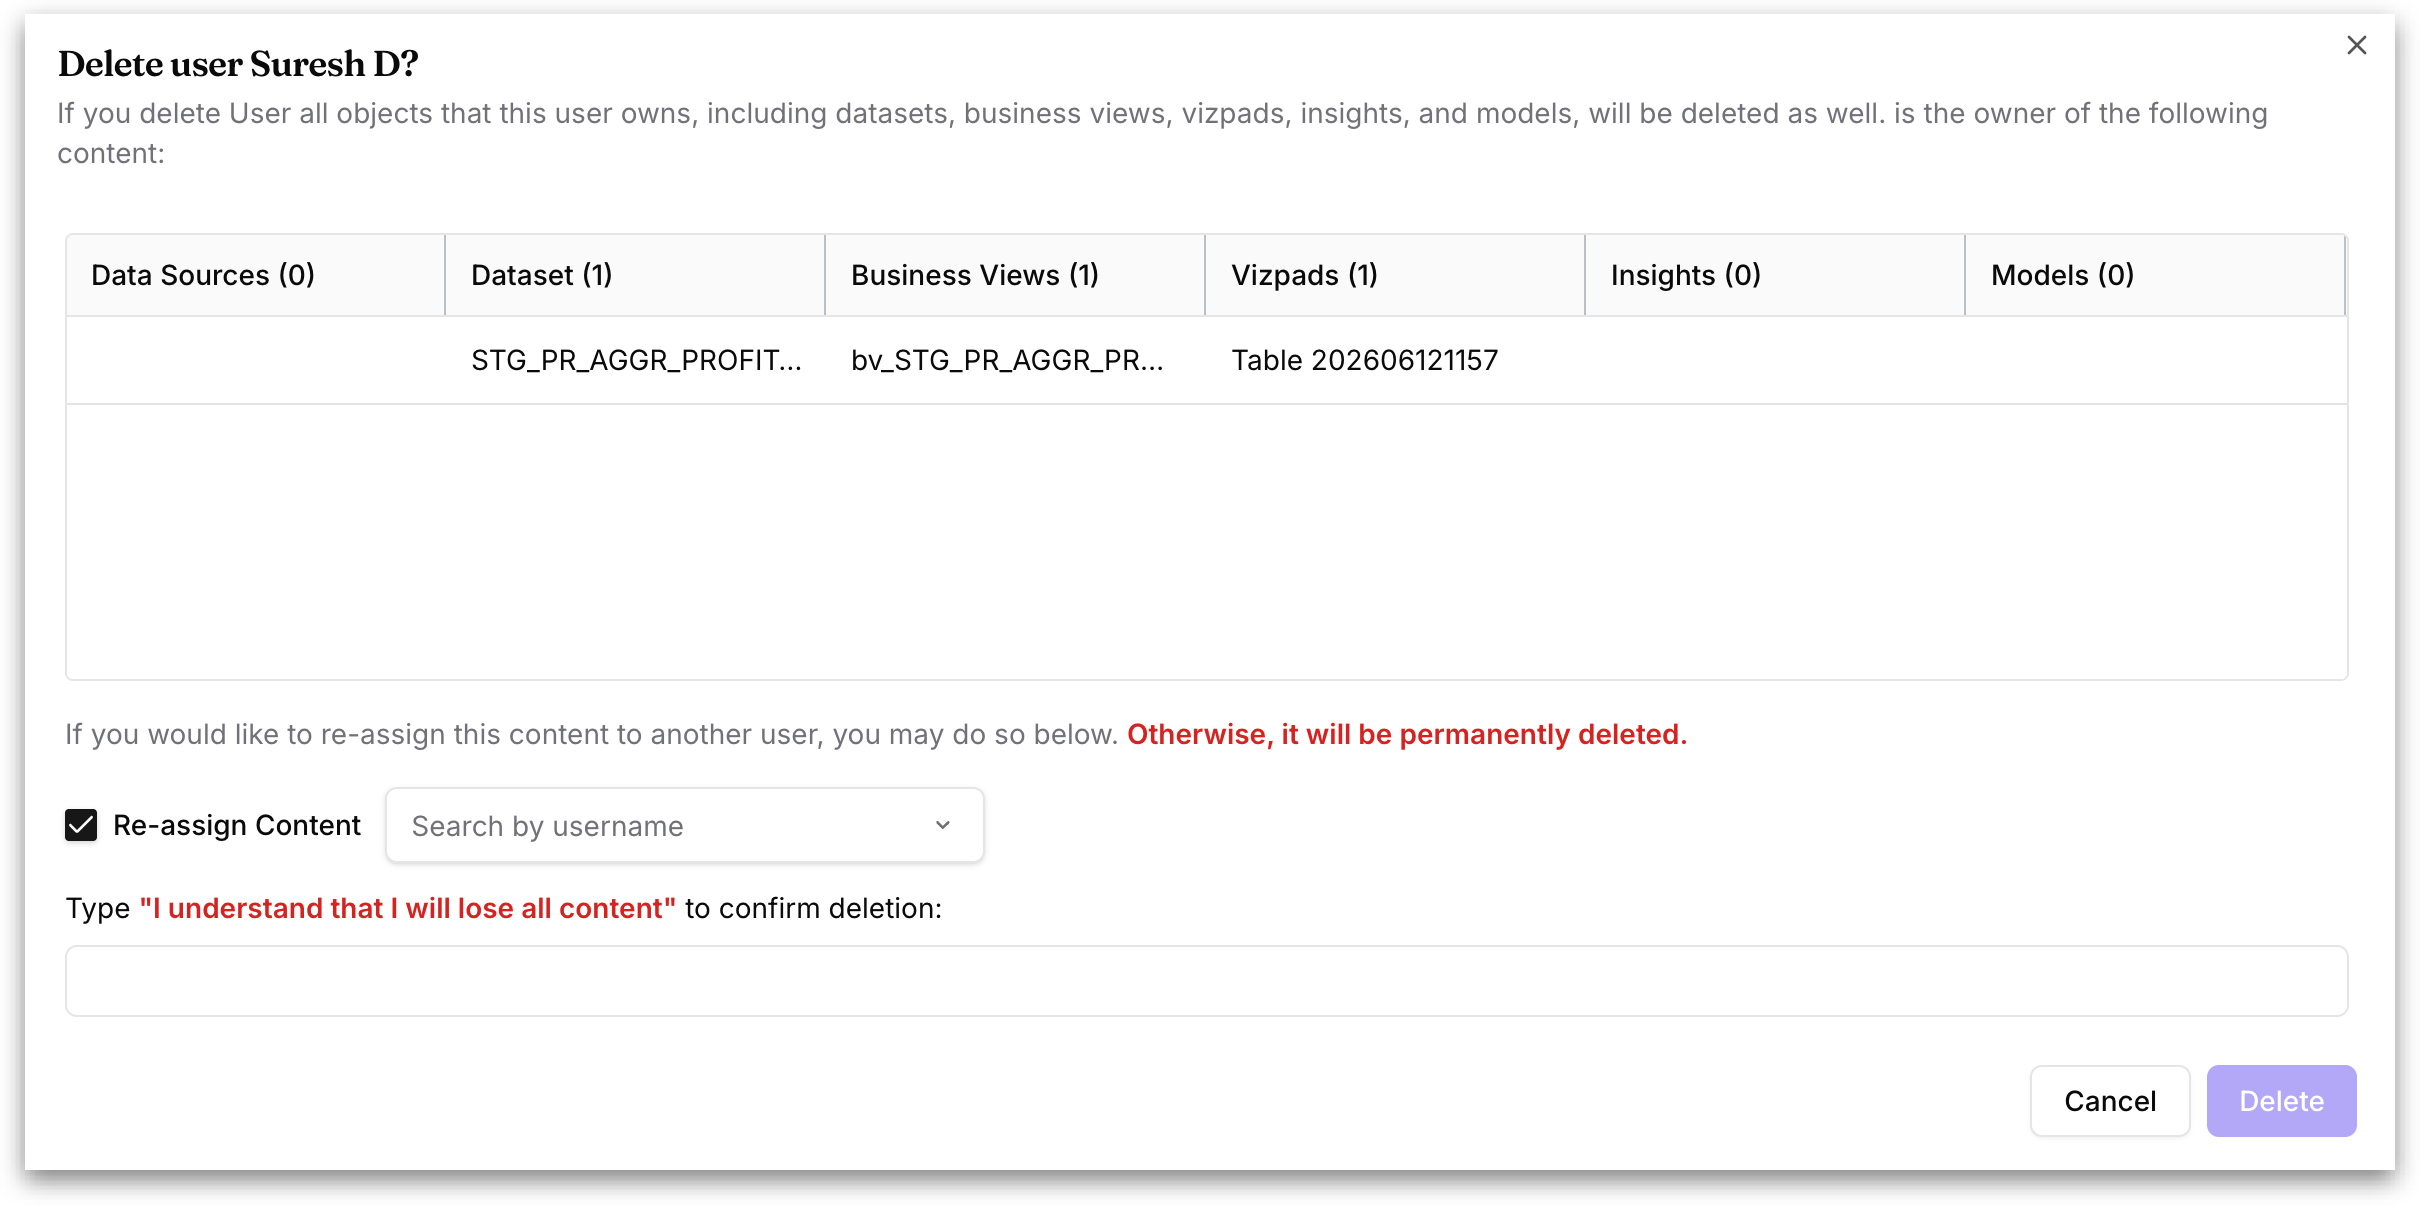
The following window will be displayed when permanently removing a user from Tellius. It provides visibility into the content owned by the user and allows safe reassignment to prevent accidental data loss.
When you delete a user, all assets owned by them (including datasets, Business Views, Vizpads, Insights, and Models) will be removed unless you reassign them to another user beforehand.
**Re-assign Content:** If enabled (checked), you can transfer all user-owned content to another user before deletion. Search and select the new owner (e.g., `jordanl`). All assets will be reassigned to this user upon deletion.
If a user is leaving your organization, reassign their content before deleting their account. Once deleted without reassignment, all listed content is permanently lost and unrecoverable.
To prevent accidental deletion, you must manually confirm your intent by typing: *"I understand that I will lose all content"*.
Only after entering this exact phrase, the **Delete** button will become active. Click on **Delete** to finalize the deletion or click on **Cancel** to dismiss.
{% hint style="warning" %}
Before you delete a user, ask your Content admin to review that user's datasets, Business Views and Vizpads, and share anything the team still needs.
{% endhint %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://help.tellius.com/tellius-6.4/settings/users-and-access/users.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.